Brown University & Cirrus Identity
Brown University extends research access to two health system partners without standing up new identity infrastructure
How Brown leveraged the Cirrus Proxy for a single, governed front door for researchers from Brown University Health and Care New England, alongside its existing InCommon authentication and a managed guest credential for outside collaborators.
At a Glance
|
Institution |
Brown University, Providence, Rhode Island |
|
Use Case |
External login for cross-institution research collaboration |
|
Products |
Cirrus Proxy with Linking, OrgBrandedID, two Proxy Connectors, OTC MFA, IDWorkflow, Identities API, Log API |
|
Authentication Sources |
Brown (via InCommon), Brown University Health, Care New England, OrgBrandedID |
The Challenge
The Brown Innovation and Research Collaborative for Health, known as BIRCH, brings researchers from Brown together with colleagues at Brown University Health and Care New England. The collaboration depends on shared systems, including Brown's Huron IRB platform for institutional review board submissions and approvals.
Federation alone could not solve the access problem. While Brown is a member of the InCommon federation, Brown University Health and Care New England is not. Their researchers carry institutional credentials at their own organizations, not at Brown. And the BIRCH collaboration also reaches outside collaborators with no affiliation to any of the three.
Brown needed a way to let 700+ researchers across four distinct populations sign in to the same set of research applications:
- Brown faculty and staff using their existing InCommon login
- Brown University Health researchers using their health system credentials
- Care New England researchers using their health system credentials
- Outside collaborators with no affiliation to any of the three institutions
The team also wanted the foundation to extend beyond the IRB system. Whatever Brown built for BIRCH would need to support additional research applications over time, with Brown owning identifier assignment so users carry a consistent Brown ID across systems.
The Solution
Brown deployed Cirrus Proxy with Managed Identities as the unified authentication layer for BIRCH research applications. The Proxy allows users to select the organization they are affiliated with and prompts them to log in using those credentials. The researcher’s identity is also linked to a Brown-assigned identifier, allowing the identity to be associated with more than one organization.
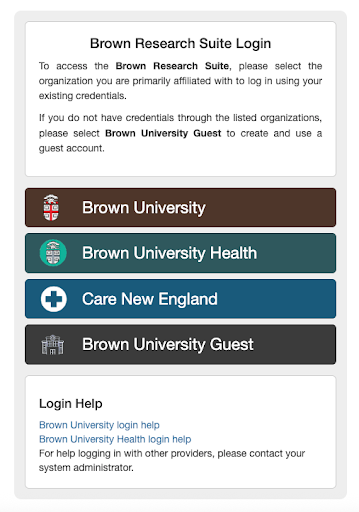
Four authentication sources, one front door
Brown faculty and staff authenticate through InCommon, the path they already use, and skip linking entirely. Researchers from Brown University Health and Care New England authenticate through Proxy Connectors configured by Cirrus to integrate with their respective institution-managed identity services. Authentication remains subject to each institution’s identity and access-management controls. Authorization to BIRCH resources is managed separately based on the researcher’s approved role and access requirements.
Identifier assignment with the Identities API
Brown wanted to own the Brown ID assigned to each non-Brown user. To meet this need, Brown was an early adopter of the new Cirrus Identities API. Brown's developers can now create and retrieve identity records programmatically, including pre-provisioning Brown University Health and Care New England users in advance so those researchers do not have to register on first use, or letting records be created at first sign-in.
Terms of service at the moment that matters
Non-Brown users complete a terms of service workflow on first sign-in. Cirrus IDWorkflow presents these terms for acceptance during onboarding. Returning users skip the workflow.
MFA where it counts
OrgBrandedID users complete one-time-code MFA on every sign-in. Brown University, Brown University Health, and Care New England all enforce MFA at their own institutions, so Brown relies on those policies rather than adding a second factor at the Proxy.
How It Works
A researcher visits the Brown IRB system. The application redirects to Cirrus Proxy, which presents a discovery screen with the four sign-in options. The researcher picks the one that matches their institution.
If they pick Brown, the Proxy routes authorization requests to the Brown Identity Provider and when the user successfully logs in, the Proxy sends the assertion to the downstream requesting application. There is no need for linking because the user already has a Brown ID.
If they pick Brown University Health or Care New England, the Proxy uses the matching Proxy Connector to facilitate sign-in at the chosen institution, runs them through the terms-of-service workflow on first use, links their account to a Brown ID, and returns them to the application.
If they pick OrgBrandedID, they either sign in with an existing account or create one, complete MFA, complete the terms workflow on first use, and link to a Brown ID.
From the application's point of view, every user looks the same: an authenticated identity with a Brown ID. The complexity stays in the Proxy.
Why This Approach Worked for Brown
Phased delivery kept Brown's developers unblocked
Cirrus and Brown ran the project in four phases over the course of 6 months.
Phase One provisioned the Linking Proxy and OrgBrandedID quickly so Brown's application team could start integration work against a real authentication source. Phase Two added the Brown University Health and Care New England Proxy Connectors. Phase Three layered in MFA, terms of service, and the Identities API. The discovery UI was also finalized during this phase. Lastly, Phase Four was testing and handoff. Brown's application development never sat waiting on identity infrastructure.
Hybrid CS and Engineering team
The Customer Success team owned everything that uses existing Cirrus capabilities and configured the IDWorkflow integration with the Proxy. The Engineering team delivered the new Identities API alpha. Brown saw one project, not two.
A foundation that extends
BIRCH and the IRB system were the first use case, not the only one. The same Proxy supports additional research applications as Brown adds them. The same Identities API supports new identifier patterns as Brown's needs evolve. New authentication sources can be added without rebuilding the front door.
Outcomes
- 700+ researchers across three institutions, plus outside collaborators, sign in to Brown research applications through one governed entry point.
- Brown owns identifier assignment. The Identities API supports pre-provisioning Brown University Health and Care New England users in advance or creating records at first sign-in, so Brown controls whether access is instant or just-in-time.
- Terms of service are enforced at the right moment without changing how Brown faculty experience login.
- Brown does not operate any new identity infrastructure. Cirrus runs the Proxy, the credential store, and the workflow engine.
The Pattern
Cross-institution research collaboration is one of the hardest external identity problems in higher education. The institutions involved often have strong individual identity programs and incompatible federation postures. Building a one-off integration for each pairing does not scale. Asking external researchers to get a sponsored campus credential creates support burden and friction.
Cirrus Proxy gives the host institution a single layer that accepts credentials from anywhere it chooses to trust, applies the policies it wants applied, and presents a clean, consistent identity to the applications behind it. Brown's BIRCH deployment is one example of the pattern. The same approach applies to research consortia, hospital and university partnerships, and any cross-institutional program where the people who need access do not all live in one identity store.
About Cirrus Identity
Cirrus Identity is a cloud-hosted identity management company built specifically for higher education and research. We work with more than 200 institutions across the US, Canada, the UK, Japan, and the UAE. Our team comes from higher ed identity, so we know InCommon, Banner, Slate, and Shibboleth from the inside. Cirrus is an InCommon Catalyst Partner.
Sign up for our quarterly newsletter to receive more stories like this!